I am not thinking of traditional supply chain attack with direct injection of malicious code in a sub component. These while they exist are exceptionally rare and we should not fret about them.
The bigger concern is a sub library have an unintentional vulnerability that could be exploited like the Log4Shell exploit of the Log4j library.
There are tools that can help in catching these vulnerabilities like BlackDuck or even GitHub to a lesser level but are they part of the process? I have no idea.
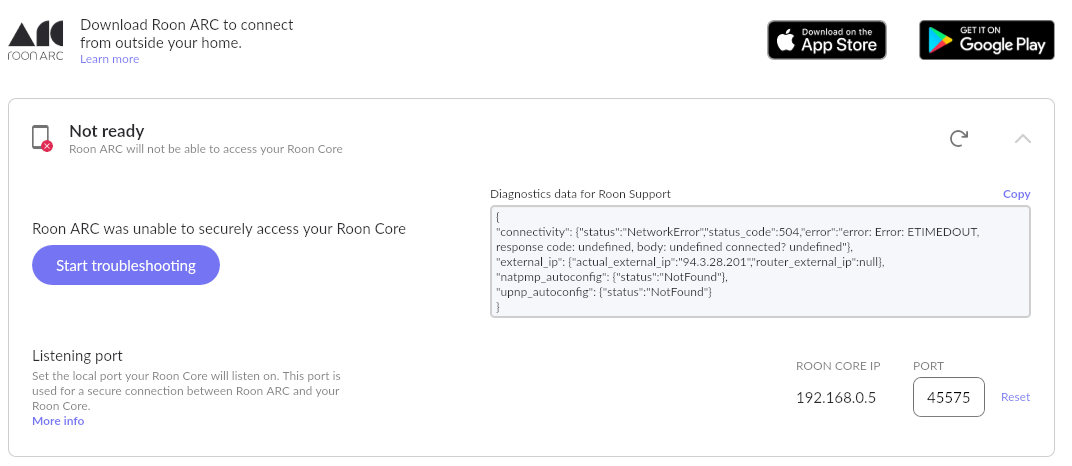
Bottom line, an open port to a device that is either sensitive or on a sensitive network is simply a bad idea. Thus before I enable this great feature (and it is great!) I will have to move my Roon core to a sacrificial server on an unimportant and separate part of my network.
Not at all. My system is pretty locked down. But, I’ve been there and around with SQL injections into software, backdoor trojans in the past. We can only do so much. As shown by the whole QNAP disaster recently. Someone will always find a way in, and sniff around to see what can be accessed.
Yes, by users exposing their networks by publishing services and having UPnP enabled and making it exceptionally easy to attack.
Hackers go for low hanging fruit.
It’s exactly the sort of hubris shown here that was exploited by the gangs operating Qlocker and Deadbolt. And they will continue to pick on those who firmly believe either “it won’t happen to me”, or, “it’s going to happen and there is nothing I can do about it”. Both mindsets are what they are looking to exploit.
1 Like
mjw
(You want nice, supportive? Call a damn helpline.)
203
Yes the logical conclusion of these kind of security discussions is that we should all just not have any computers and never use the internet. Thats secure
So, do I understand correctly that running ROCK on a separate NUC only exposes this NUC to potential security risks from opening a port for ARC, however small these risks may be? Or could Rock potentially be infected in a way that other devices/shares on the network also become accessible for outside attacks?
Should Roon maybe recommend a separate roon server device for people using Arc, given such security issues?
I think ROCK on a separate device (NUC) is probably the best option from a security perspective. Unless you intend to go to the lengths that some here recommend of DMZs, sacrificial servers and isolated VLANs. Which IMO are not really necessary.
Theoretically something malicous could jump from your NUC running ROCK to another device but the chances of this seems very small.
Yep that is it… for your information as well, after changing it to 0, each time I have restarted the core since installing 2.0 the 0 is replaced by the port no. that originally appeared there… so just in case, I go to settings each time and put it back to 0.
You could always just select your own random port?
With such a small amount of users and such a random application is someone really going to go hunting for them?
On my NAS it shows zero attempted logons since it was installed.